Scheduled launch
Goes live Week 44, 2026
October 26 - November 1, 2026 · Leaderboard opens Monday 00:00 UTC
00
Days
00
Hours
00
Mins
00
Secs
Upvotes
Unlocks at launch
Dofollow backlink
Unlocks at launch
Leaderboard
Unlocks at launch
Comments
Unlocks at launch
Reviews
Unlocks at launch
Voting opens Week 44, 2026
Upvotes unlock when the launch week starts
Comments open at launch
Discussion unlocks with the leaderboard
About InsurStaq AI
Gallery
Demo video
Overview
Who is it for?
CTOs and engineering teams facing SOC 2 or ISO 27001 audits, AppSec and compliance teams, and security consultancies
Problem
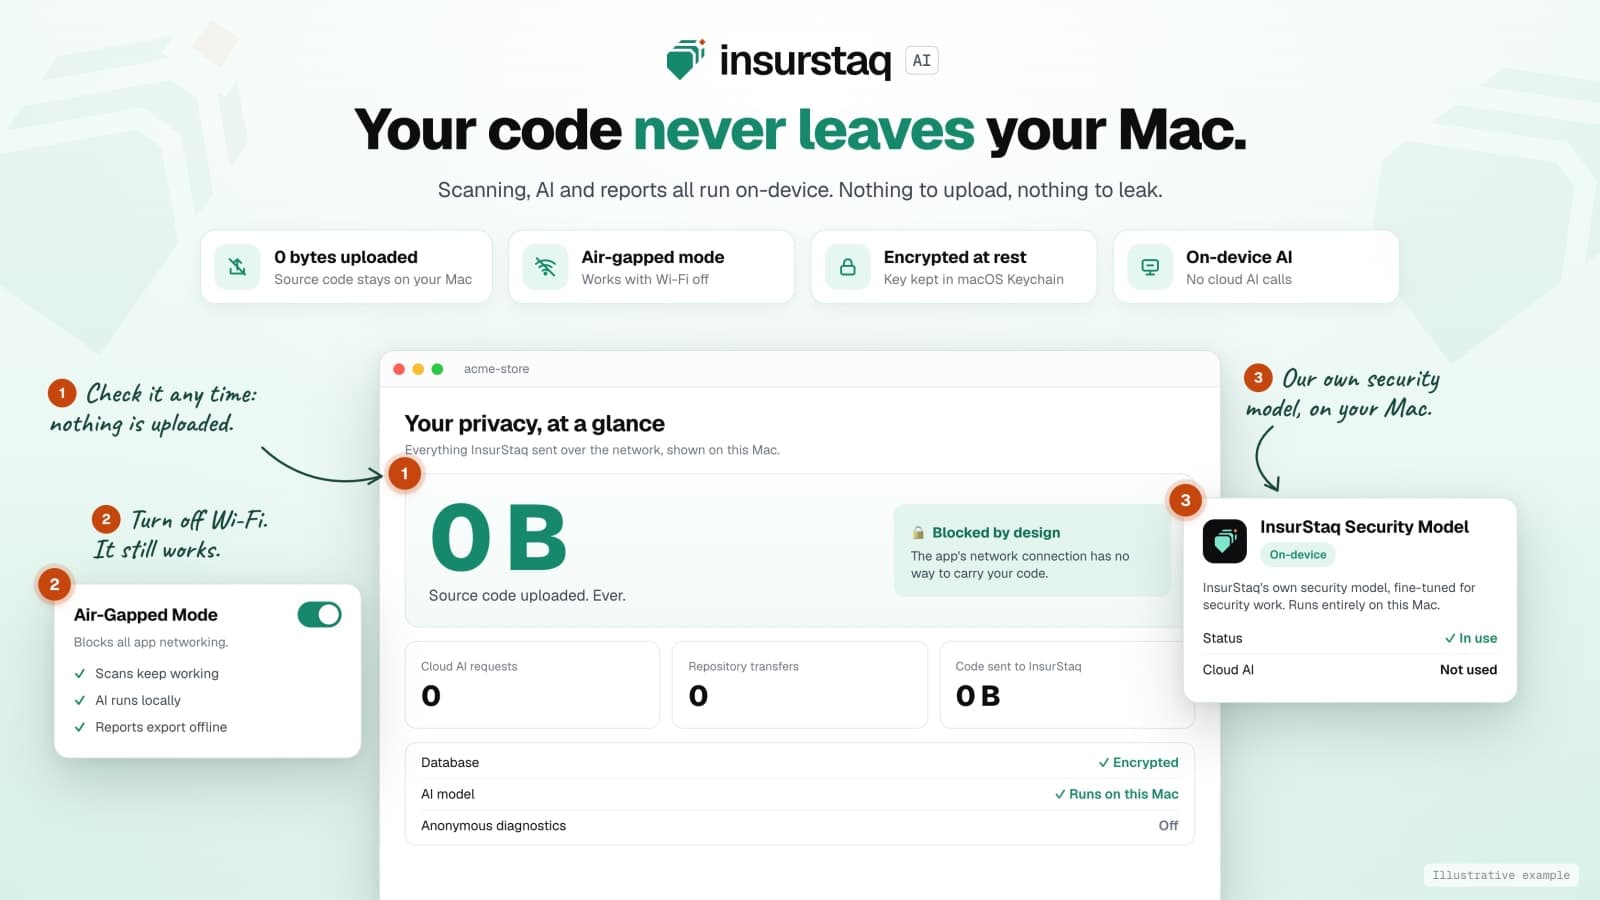
Most scanners hand you a long list of findings with a file and a line number. Teams cannot tell which ones an attacker can actually reach, fixing them is slow, and many tools need your source code uploaded to someone else's cloud.
Solution
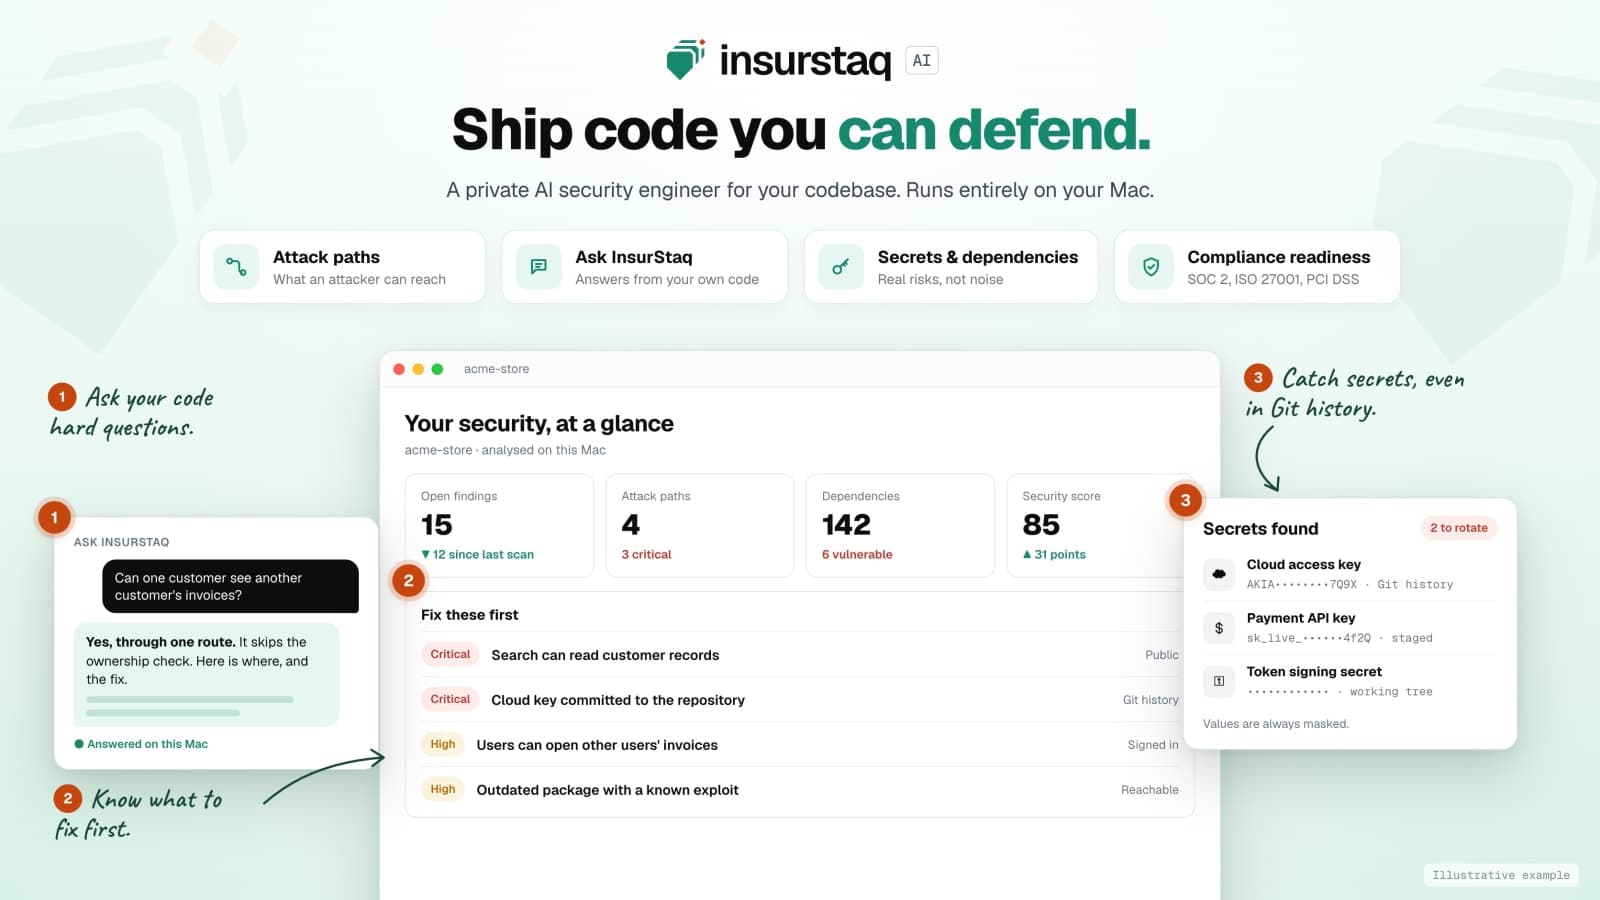
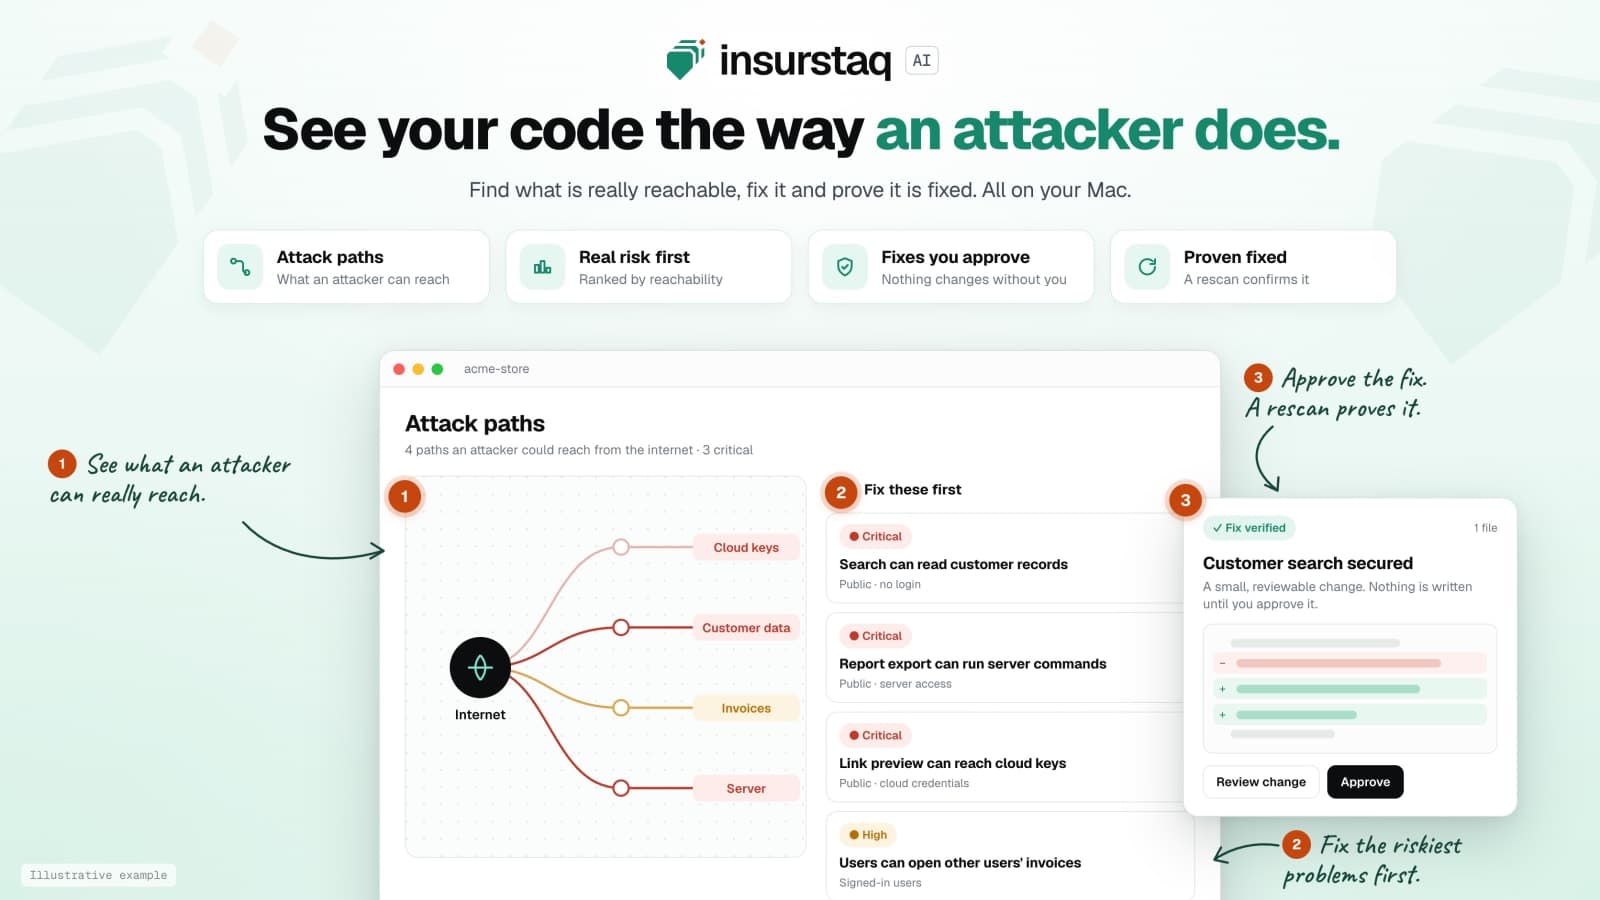
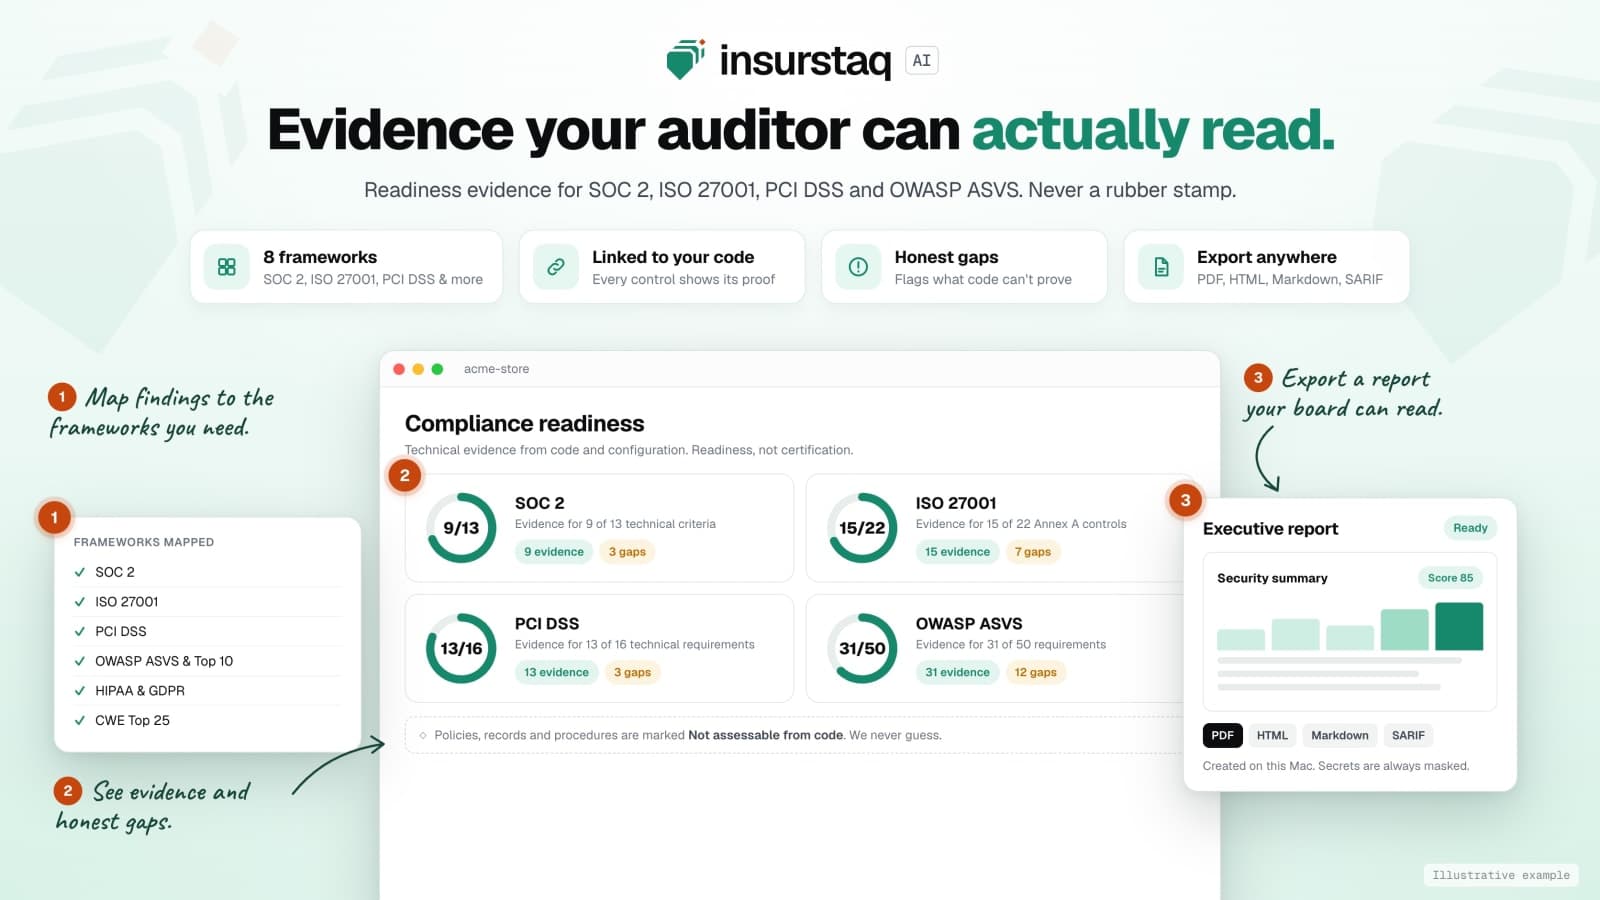
InsurStaq runs on your Mac. It shows the attack paths an attacker could really reach, from the internet to the exact line, and ranks real risks first. It drafts a fix you approve, a rescan proves the path is gone, and the evidence maps to SOC 2, ISO 27001, PCI DSS and OWASP ASVS readiness.
What makes it unique
Attack paths instead of lists, a fix you approve with a rescan that proves it worked, and audit-ready evidence. All without a single line of your code leaving your laptop: zero bytes of source code uploaded.